This challenge is from the Love at First Breach Valentine event on TryHackMe.
Challenge title: TryHeartMe
Category: Web
Difficulty: Easy
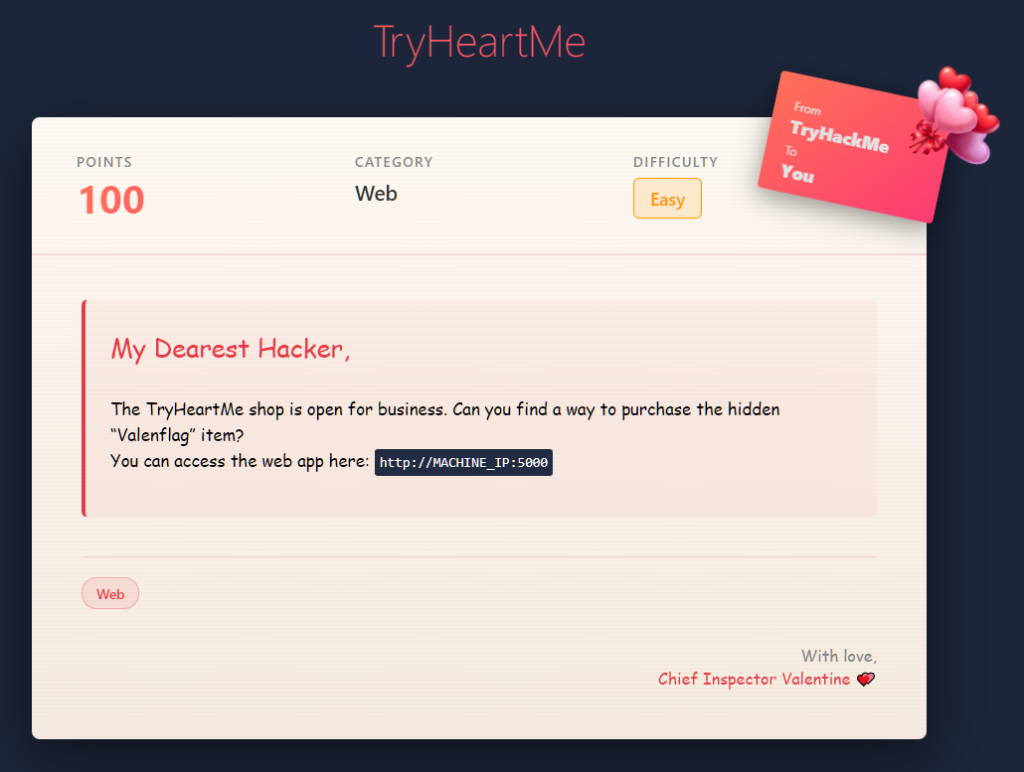
The objective of this challenge is to purchase the hidden Valenflag item from the web shop. I started by opening the challenge URL (port 5000) and monitoring traffic with Burp Suite to understand request and response behavior.
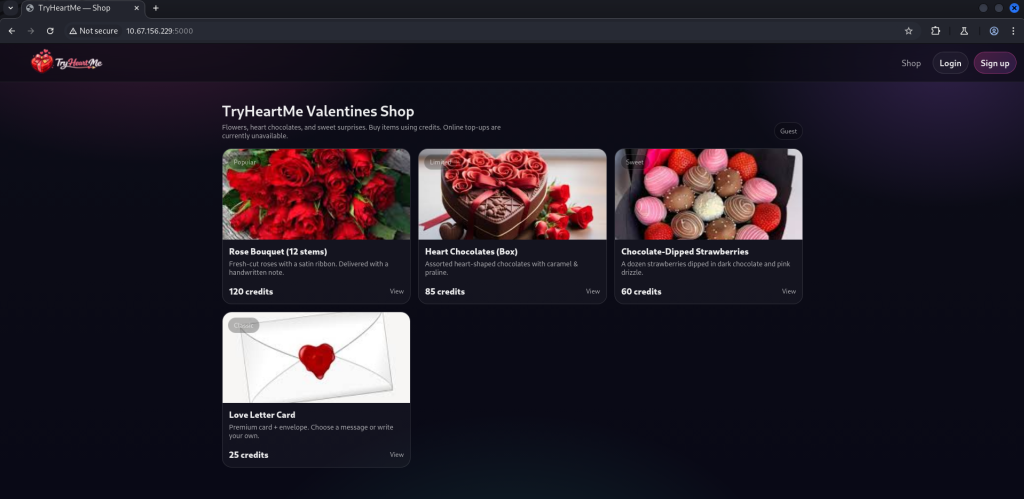
The target application is a Valentine-themed online store. I created a new account and tried buying a normal item first to understand the purchase flow before testing anything unusual.
A fresh account starts with 0 credits, so any purchase fails immediately due to insufficient balance.
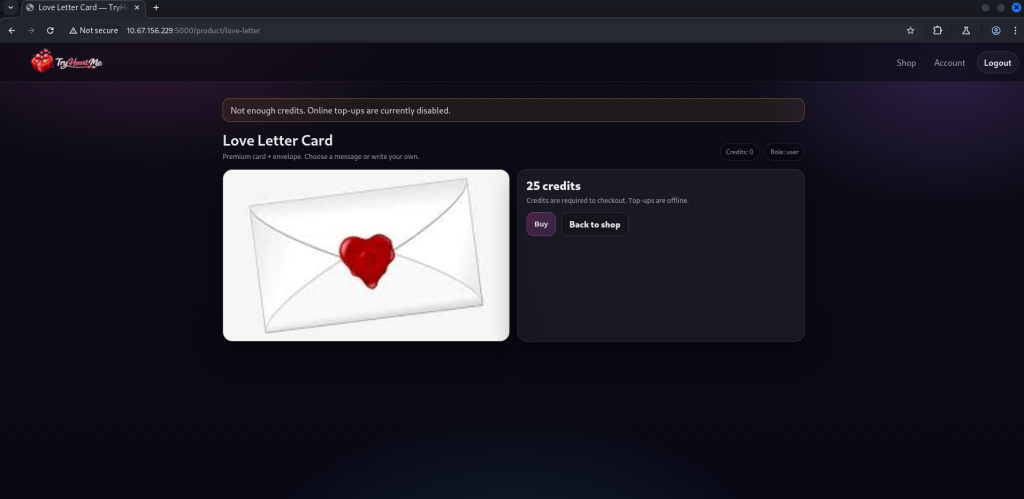
My first attempt was to tamper with the buy request and directly purchase the hidden item. That failed because no product with the valenflag slug was available to my current user context.
At that point, I shifted to analyzing the JWT to see whether I could escalate privileges or increase credits by modifying the data stored inside the token.
Since a JWT consists of three Base64URL-encoded parts (header, payload, signature) separated by dots, I first Base64URL-decoded the header and payload to inspect their contents. After decoding, I found useful fields such as role and credits:
{"alg":"HS256","typ":"JWT"}{"email":"test1@test.com","role":"user","credits":0,"iat":1771015120,"theme":"valentine"}0R0'(nPu-0?Y
The presence of role and credits in the payload indicated that privilege and balance were being enforced client-side via token claims.
I then modified the token by changing the algorithm from HS256 to none, removed the signature entirely, set role to admin, and increased credits to 9999. After making these changes, I Base64URL-encoded the modified header and payload again and reconstructed the token without a signature.
Using this forged token against /account confirmed the privilege escalation, as the server accepted the manipulated claims and granted elevated access.
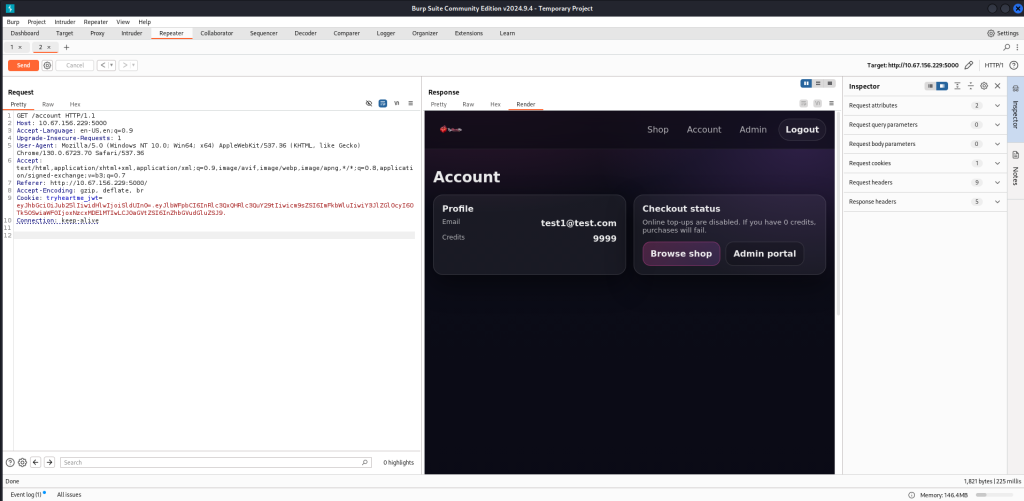
The JWT attack worked: I now had admin access and enough credits to continue.
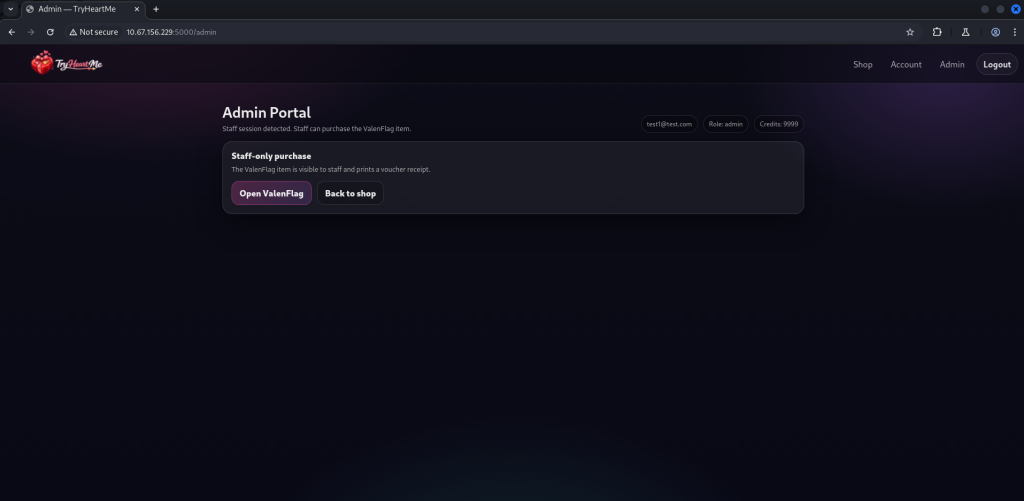
With the modified JWT set as the cookie, visiting /admin exposed the admin portal, including an option for the hidden item.
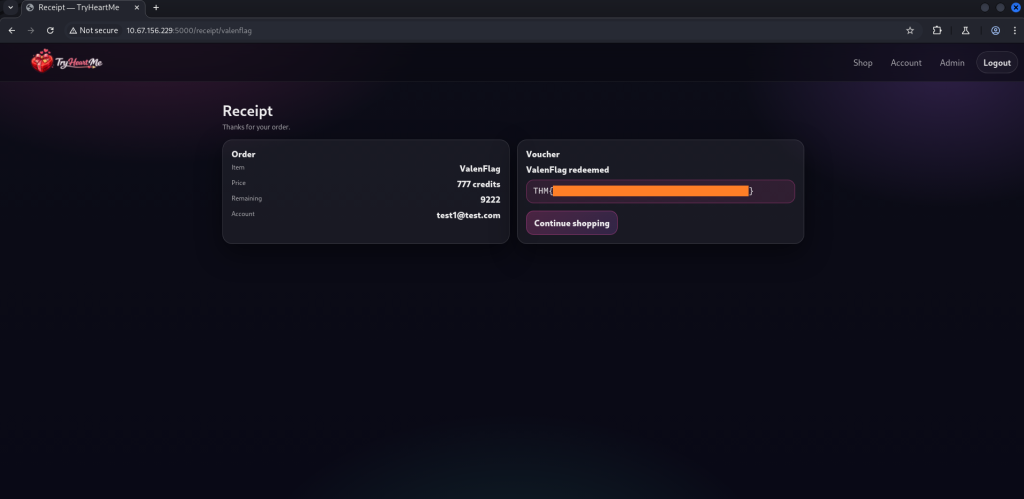
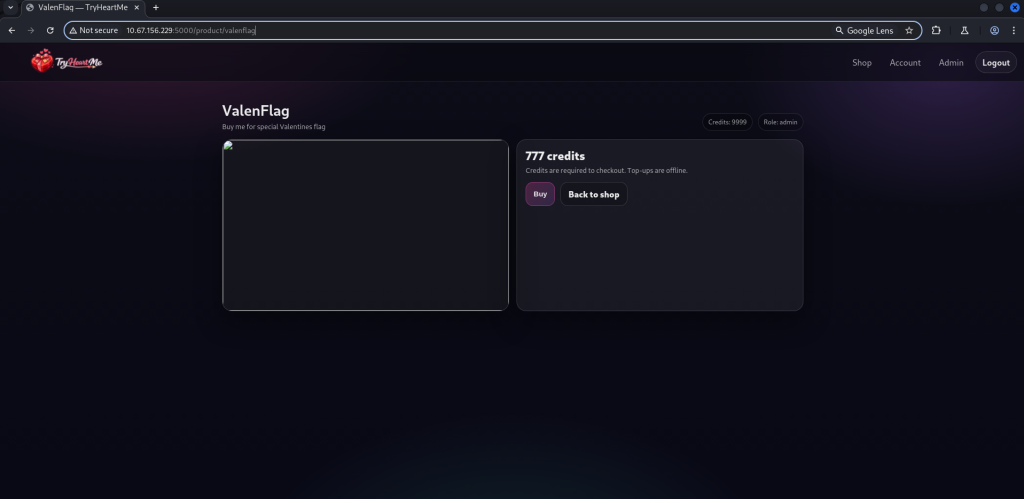
That action led to /product/valenflag, which became accessible with the admin role. The item price was 777 credits, which I could now afford.
After purchasing, I was redirected to /receipt/valenflag, where the flag appeared in the voucher section.