This challenge is part of the Love at First Breach Valentine event on TryHackMe.
Challenge title: Hidden Deep Into my Heart
Category: Web
Difficulty: Easy
I started with a quick service scan using nmap.
nmap -sV [MACHINE_IP]
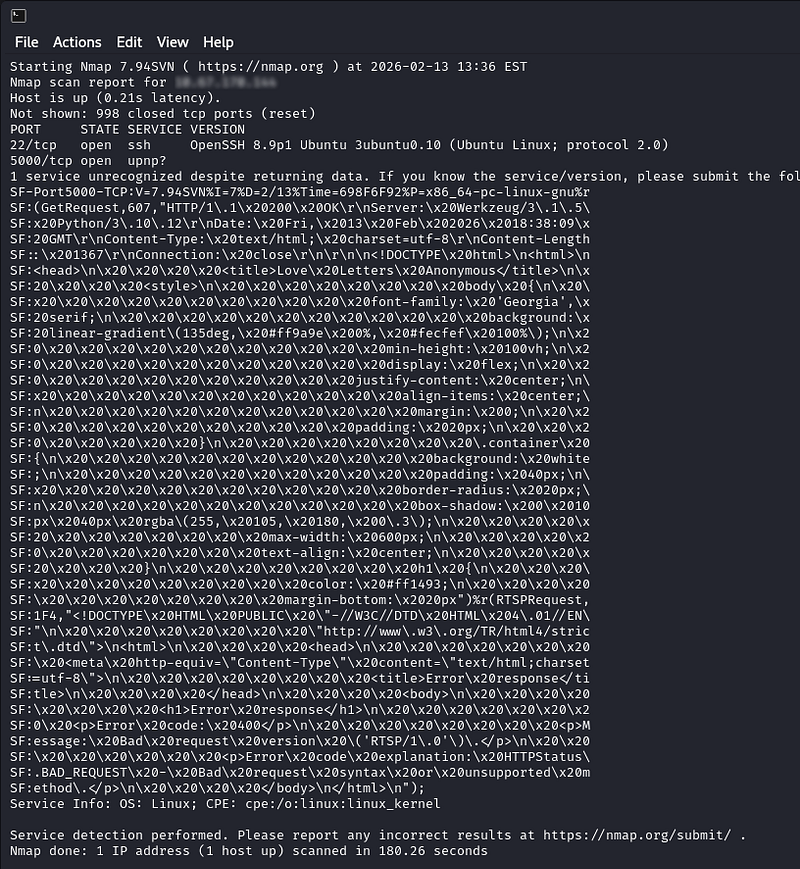
The main target was on the port 5000.
The fingerprint (Server: Werkzeug/3.1.5 Python/3.10.12) indicates a Python web app, likely Flask.
Next, I browsed the app and monitored requests/responses with Burp Suite proxy.
The homepage describes a secret Valentine message board, but it has no visible links or actions.
Love Letters Anonymous

Welcome to our secret valentine message board!

Share your anonymous love letters with the world...
A good next step was checking robots.txt.
/robots.txt was available and gave the first clue.
User-agent: *
Disallow: /cupids_secret_vault/*

# cupid_arrow_2026!!!
From this file, we got the path /cupids_secret_vault/.
It also exposed a useful comment value: cupid_arrow_2026!!!.
Visiting /cupids_secret_vault/ showed another page with a hint-like message.
Cupid's Secret Vault

You've found the secret vault, but there's more to discover...
There were still no links.
Since robots.txt used /cupids_secret_vault/*, the next move was directory enumeration under that path.
I used ffuf to brute-force hidden endpoints.
ffuf -u http://[MACHINE_IP]:5000/cupids_secret_vault/FUZZ -w /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt
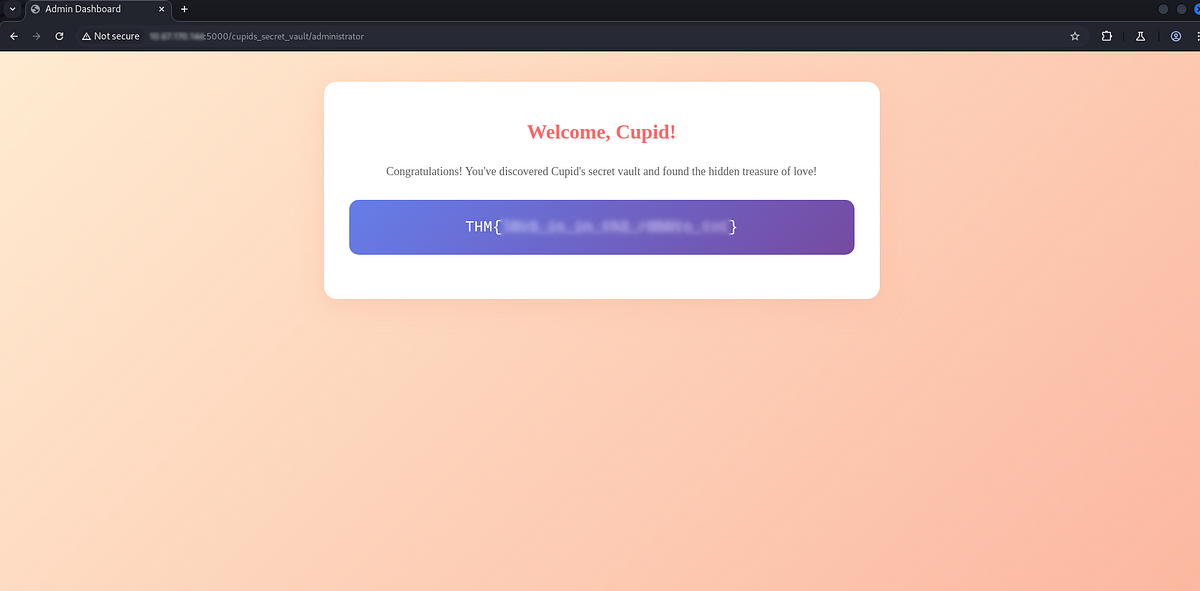
Enumeration revealed /administrator, which is an admin login page.
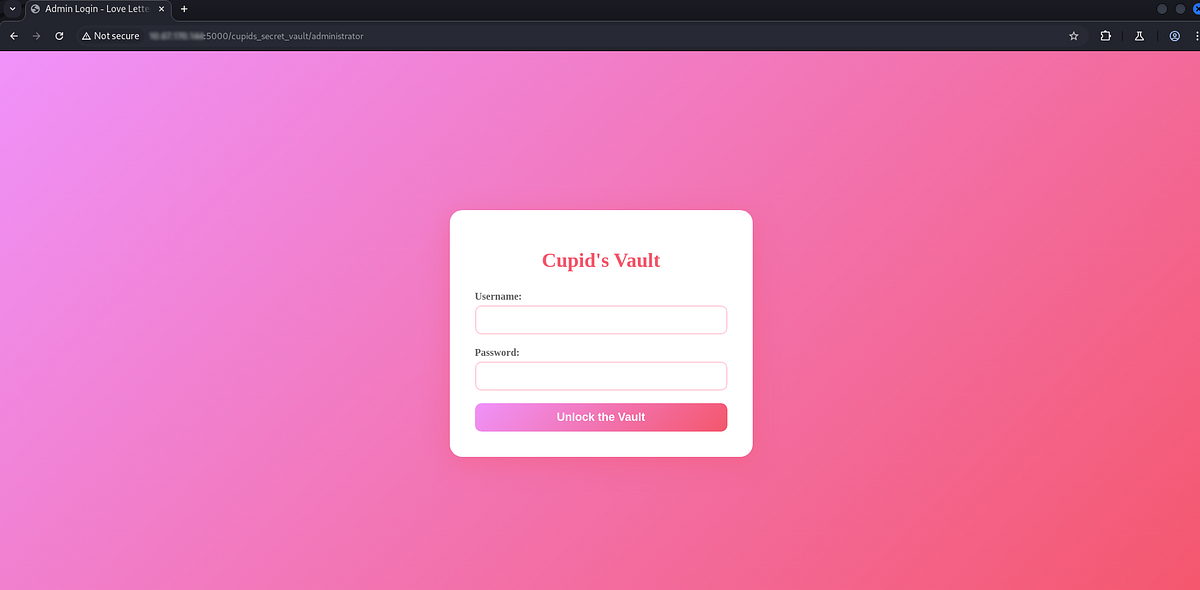
I then tried common admin usernames with the value from robots.txt as the password.
admin worked on the first attempt, and I got access to the vault and captured the flag.